Use the Prompt
Add Your Brief
Add your context below. It will be included with the prompt when you copy or download.
Create an interactive frontend prototype using the existing project stack and explicitly labeled demo data for [PROJECT] and [AUDIENCE]. The task is: API Key Management.
Required content and structure
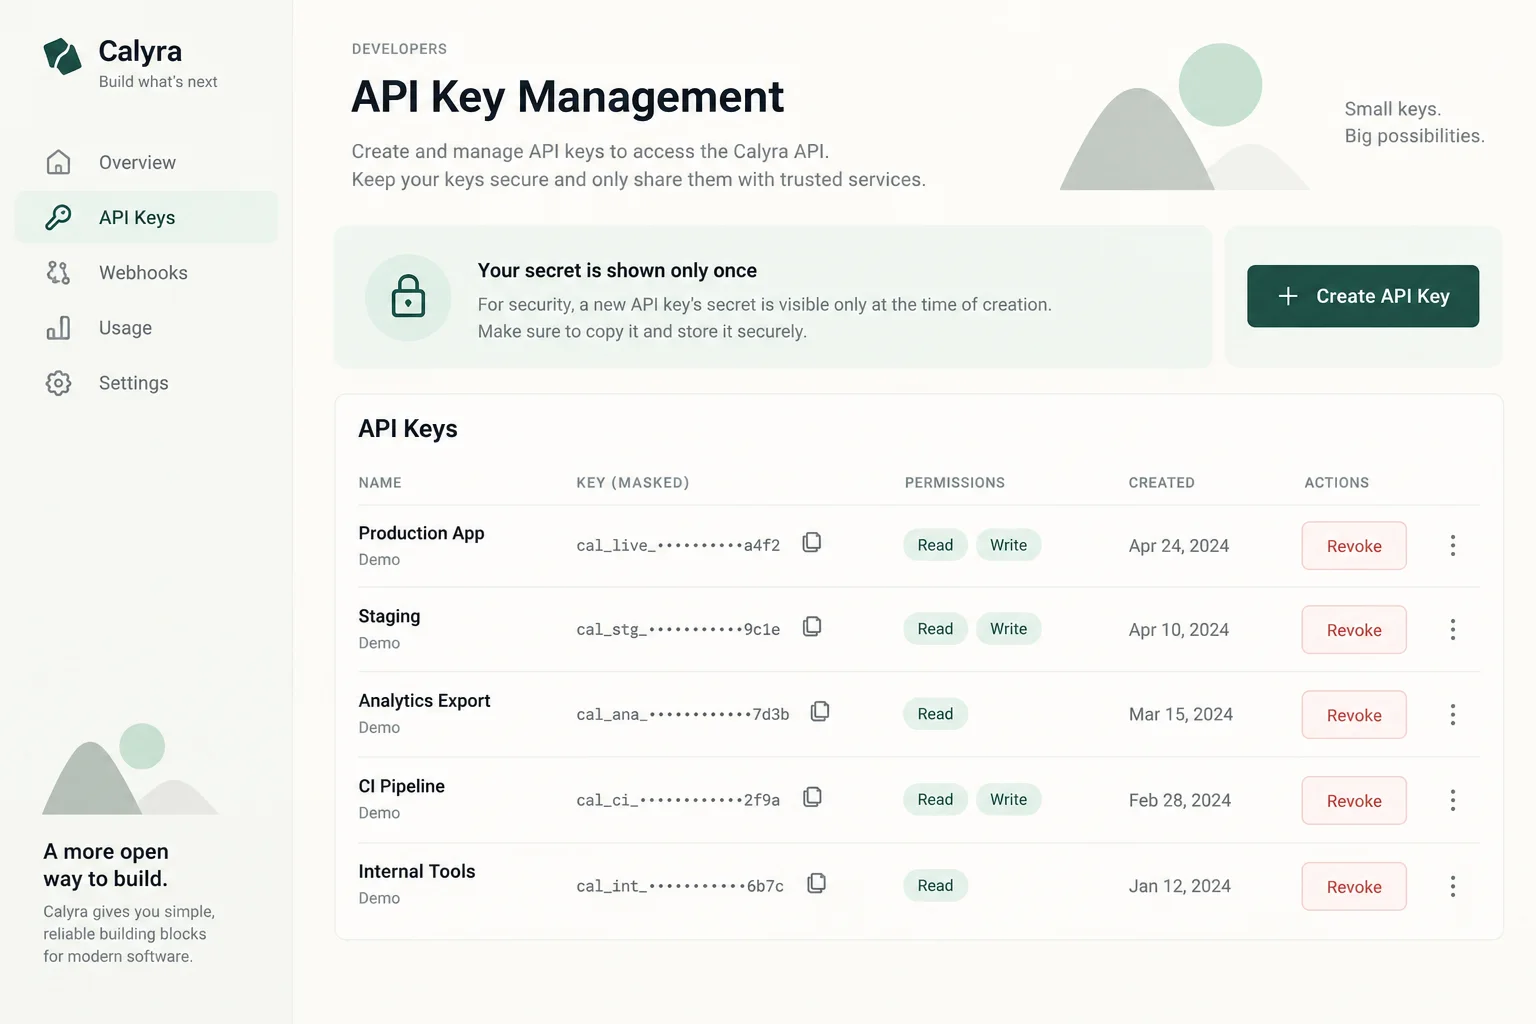
List named keys, permissions, creation dates and revoke actions.
Use [APPROVED_CONTENT] as the source of names, dates, figures, claims and destinations. List missing inputs before substituting anything. If a demonstration is needed, label its content as fictional. Do not invent customer quotes, rankings, partner logos or product capabilities.
Design direction
Use [BRAND_RULES] and the design system already selected in the project. If no system is supplied, start with this direction: warm white, ink text and restrained mint selected states; generous spacing and simple controls. Keep type, spacing and color roles consistent. Prioritize the task over decorative elements and avoid a generic collection of unrelated cards.
Content preparation
Define key names, scopes, creation dates, last-used display and revocation behavior. Use masked sample tokens and explain the one-time reveal rule for newly created keys.
Layout and behavior
Separate creating a key, viewing its permissions and revoking it. Keep the secret out of list views and make the revoke confirmation identify the selected key.
Task-specific acceptance check
- Display masked examples only and make one-time secret visibility explicit.
- Test an unused key, a long name and a failed revocation.
- A displayed success must reflect the action result, and reopening an existing key must not reveal a secret that is no longer available.
Implementation and review
Keep text editable. Use semantic structure, descriptive controls, visible keyboard focus and appropriate empty/error states. Check narrow and wide layouts. Respect reduced-motion preferences. Preserve any existing project framework and dependencies; do not silently replace the stack. Return the editable files and explain any incomplete behavior or unsupported inputs. Review this specific task before proposing extra features.
Reference attachment and reconstruction goal
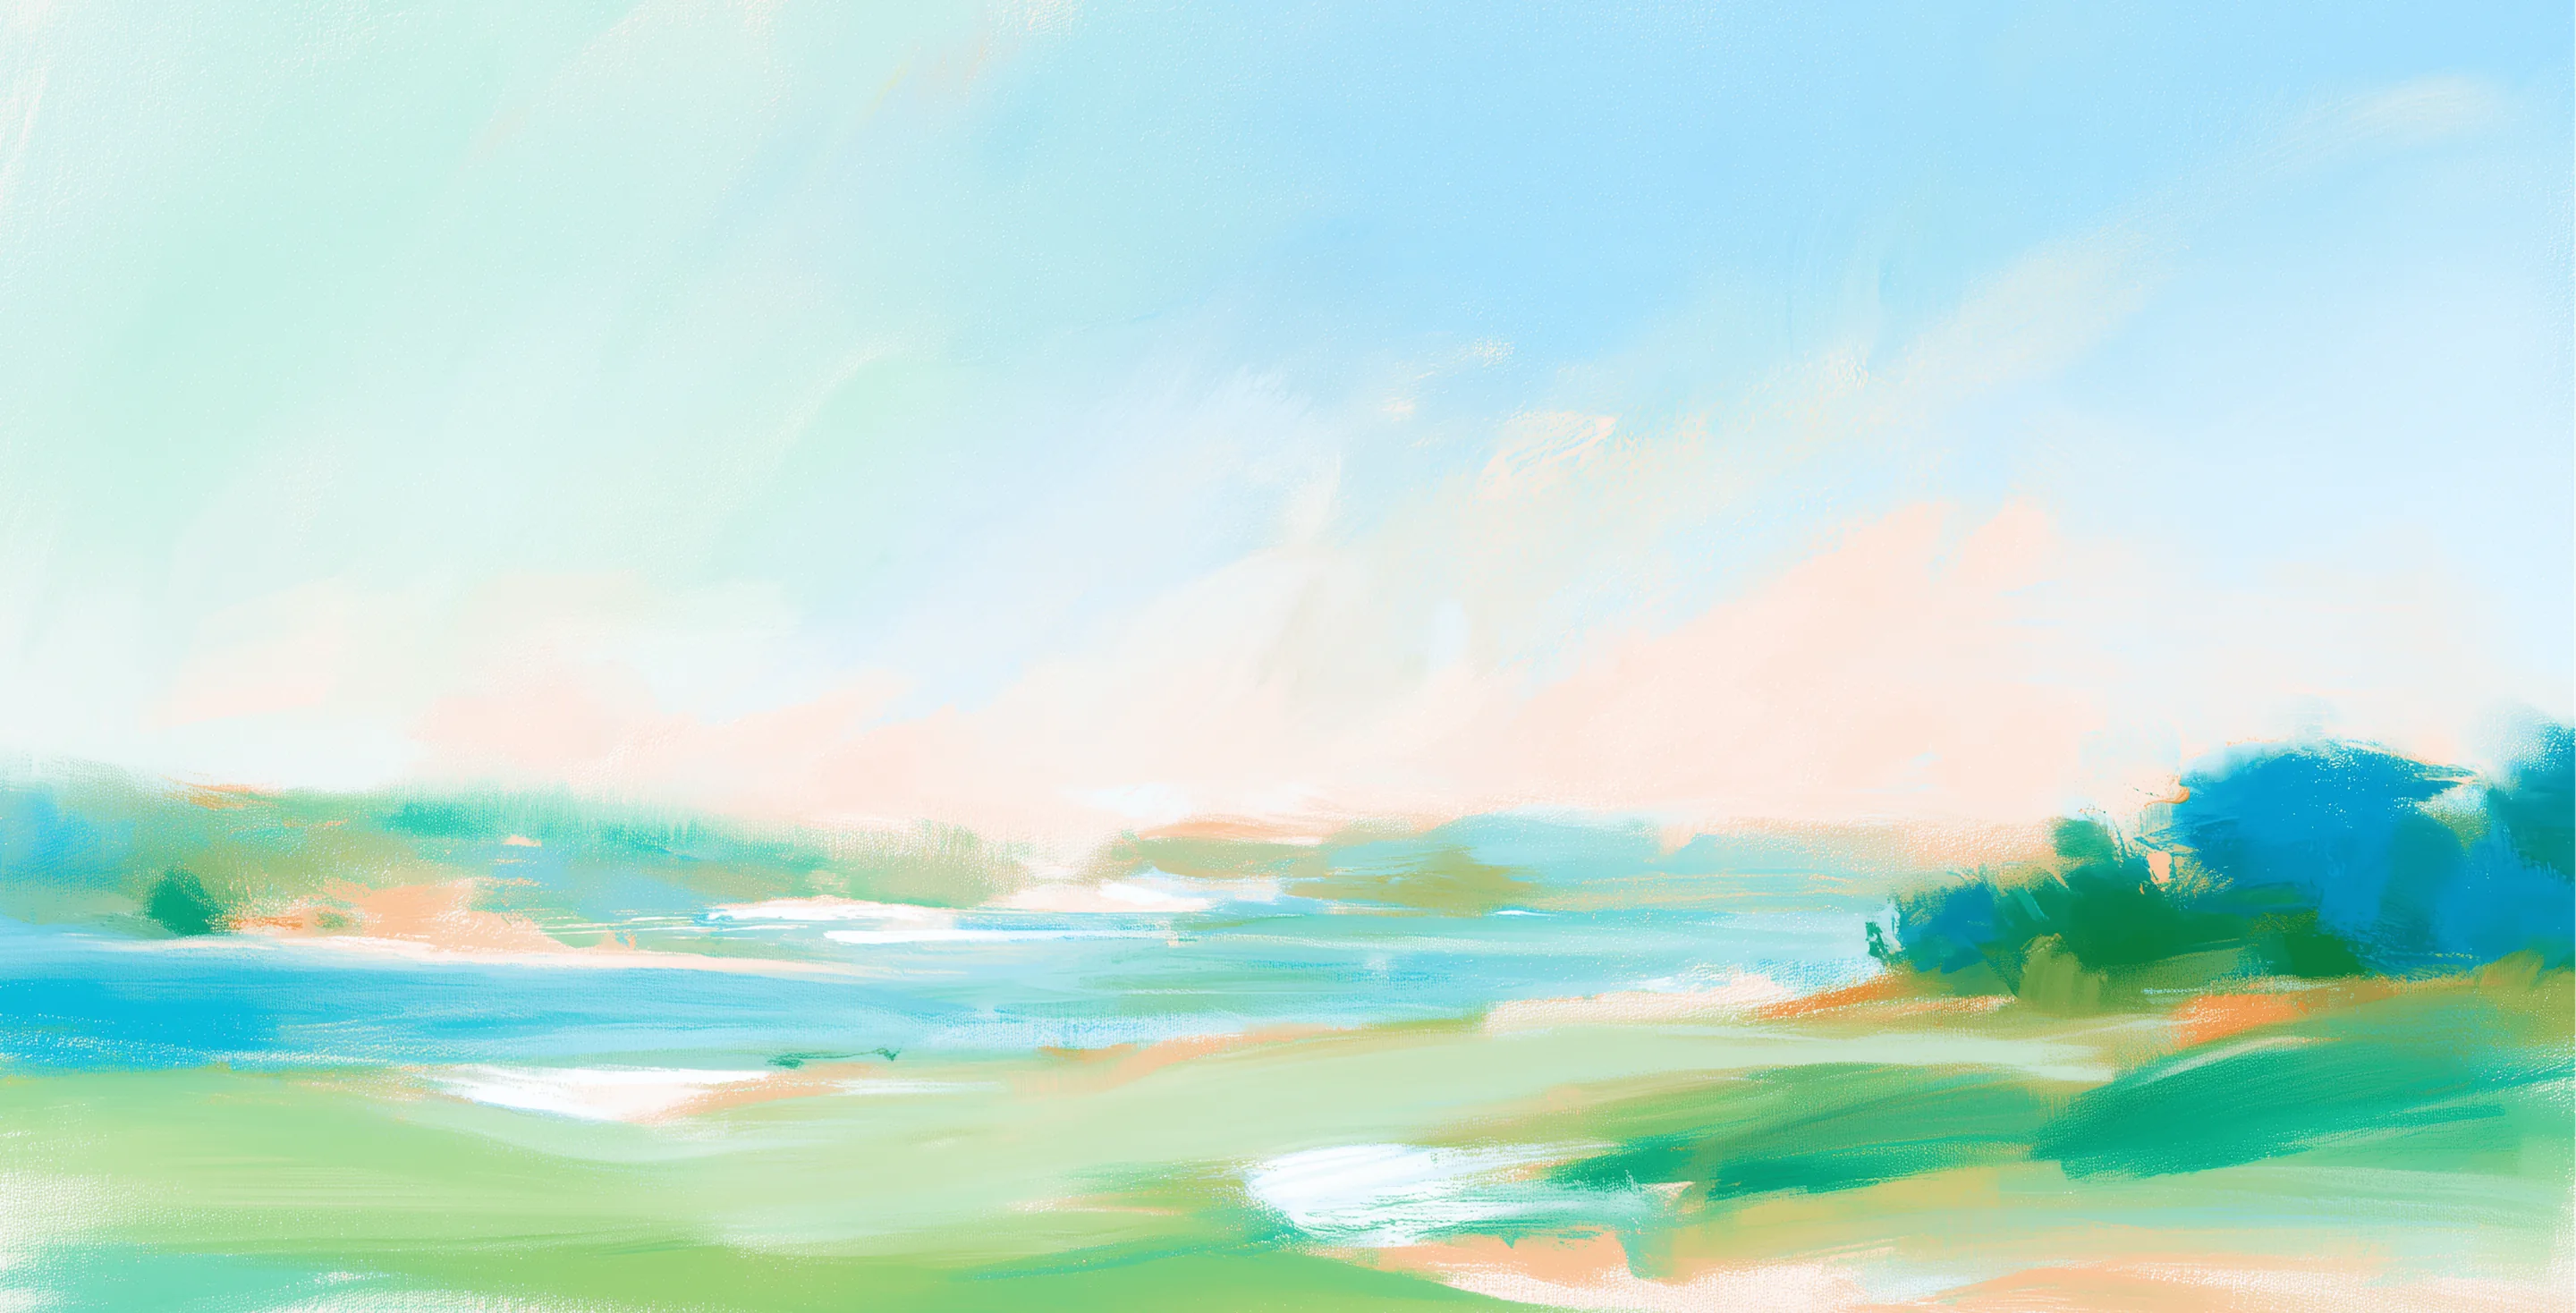
Attach reference.webp from this prompt’s download bundle alongside this prompt in OpenDesign. Build an editable result with a similar composition and hierarchy; do not embed the whole reference image as the finished interface. Preserve approved project content and brand rules if they conflict with fictional sample labels. If the image is missing or unreadable, ask for it instead of claiming visual fidelity.
Reference composition and content
Use the attached reference.webp as the visual reference for API Key Management. Before building, identify the major regions from top to bottom, their relative widths and heights, alignment, spacing, typography hierarchy, surface colors, borders, imagery and repeated components. Preserve those relationships rather than substituting a generic template. Required task content: List named keys, permissions, creation dates and revoke actions. Use the following task-specific layout guidance when translating the image into editable elements: Separate creating a key, viewing its permissions and revoking it. Keep the secret out of list views and make the revoke confirmation identify the selected key.
Visual direction from the example brief
warm white, ink text and restrained mint selected states; generous spacing and simple controls.
Interaction specification
The reference is a static concept: the behavior below is a requirement to implement, not proof that the picture already works. Copy the customized prompt into your working project. Start with the core task: List named keys, permissions, creation dates and revoke actions. Display masked examples only and make one-time secret visibility explicit. For each visible control, specify its trigger, affected state and feedback; implement local changes with consistent state across related views. Give search and filters real results, selection controls an explicit active state, and save actions visible pending/success/failure feedback where relevant. Do not add unrelated workflows. Use proper links for navigation, buttons for actions and accessible names for icon controls. Do not imply a backend operation succeeded when only a local demo changed.
Visual comparison and delivery
- Compare the result with the attached image at matching proportions. Review major region placement, relative image sizes, line breaks, spacing, typography hierarchy, contrast, active states and content density before polishing decorative details.
- Then test the narrow layout without squeezing desktop text into tiny labels.
- Keep logos, photos and icons as separate assets and all meaningful labels editable. List any unavailable fonts/assets and any intentional departures. Return the working files plus a concise account of implemented behavior and remaining integrations; do not promise a pixel-identical result from the prompt alone.
Download Prompt + Image
Includes the complete prompt and full-size reference image. Attach both in OpenDesign to guide the layout.
How to Write an API Key Management Design Prompt
Use this api key management design prompt to list named keys, permissions, creation dates and revoke actions.
The reference is an AI-generated concept. The instructions below describe what to build and test; the image does not demonstrate working behavior.
Design for the Secret's Lifecycle
An API key management screen needs to explain creation, one-time visibility and revocation.
The key list should help identify credentials without exposing their secret values. Separate creating a key, viewing its permissions and revoking it. Keep the secret out of list views and make the revoke confirmation identify the selected key.
From the Prompt
Separate creating a key, viewing its permissions and revoking it.
Make It Your Own
List named keys with permissions and creation dates using masked examples. Show a one-time reveal on creation and explain the consequence before revoking [KEY_NAME].
Prepare the API Key Management Content
The table shows key names, masked identifiers, permissions and creation dates. Provide these fields without placing usable secrets in the page or its sample data.
Define key names, scopes, creation dates, last-used display and revocation behavior. Use masked sample tokens and explain the one-time reveal rule for newly created keys.
From the Prompt
List named keys, permissions, creation dates and revoke actions.
Make It Your Own
For [PROJECT], use [APPROVED_CONTENT] as the source for this api key management. Define key names, scopes, creation dates, last-used display and revocation behavior. Use masked sample tokens and explain the one-time reveal rule for newly created keys. Identify missing inputs before replacing them with demonstration content.
Return After Creation
The notice explicitly says a secret is shown only once, next to Create API Key. Implement that reveal-and-copy flow and test recovery messaging without exposing existing keys again.
The secret should no longer be recoverable from the list unless the supplied product behavior explicitly supports it. The interface should explain how to replace a lost key. Test an unused key, a long name and a failed revocation. A displayed success must reflect the action result, and reopening an existing key must not reveal a secret that is no longer available.
From the Prompt
Display masked examples only and make one-time secret visibility explicit.
Make It Your Own
Review the api key management against this requirement: Display masked examples only and make one-time secret visibility explicit. Test an unused key, a long name and a failed revocation. A displayed success must reflect the action result, and reopening an existing key must not reveal a secret that is no longer available. Preserve approved content and revise only the parts that fail this check.
Review Your API Key Management Result
A convincing screen is not a working backend. Test validation, permissions, persistence and failure behavior separately before connecting real data.
- Test an unused key, a long name and a failed revocation. A displayed success must reflect the action result, and reopening an existing key must not reveal a secret that is no longer available.
Follow-Up Prompt
Use this after the first result. It narrows the revision to the most important part of this task.
Refine the current api key management. Test an unused key, a long name and a failed revocation. A displayed success must reflect the action result, and reopening an existing key must not reveal a secret that is no longer available. Preserve the approved content and visual direction; change only the parts needed to resolve these issues.